Post-Quantum Ready: Why Europe’s Connected Vehicles Need Future-Proof Encryption Today
Post-quantum cryptography for connected vehicles is becoming a priority. How can Europe secure vehicles built to last decades? Patricia Trinkaus of eco explains.

Patricia Trinkaus
As vehicles become increasingly software-defined, connected and autonomous, cybersecurity is becoming fundamental to safe and trustworthy mobility. With vehicles designed to operate for decades, today’s security decisions will have consequences far into the future.
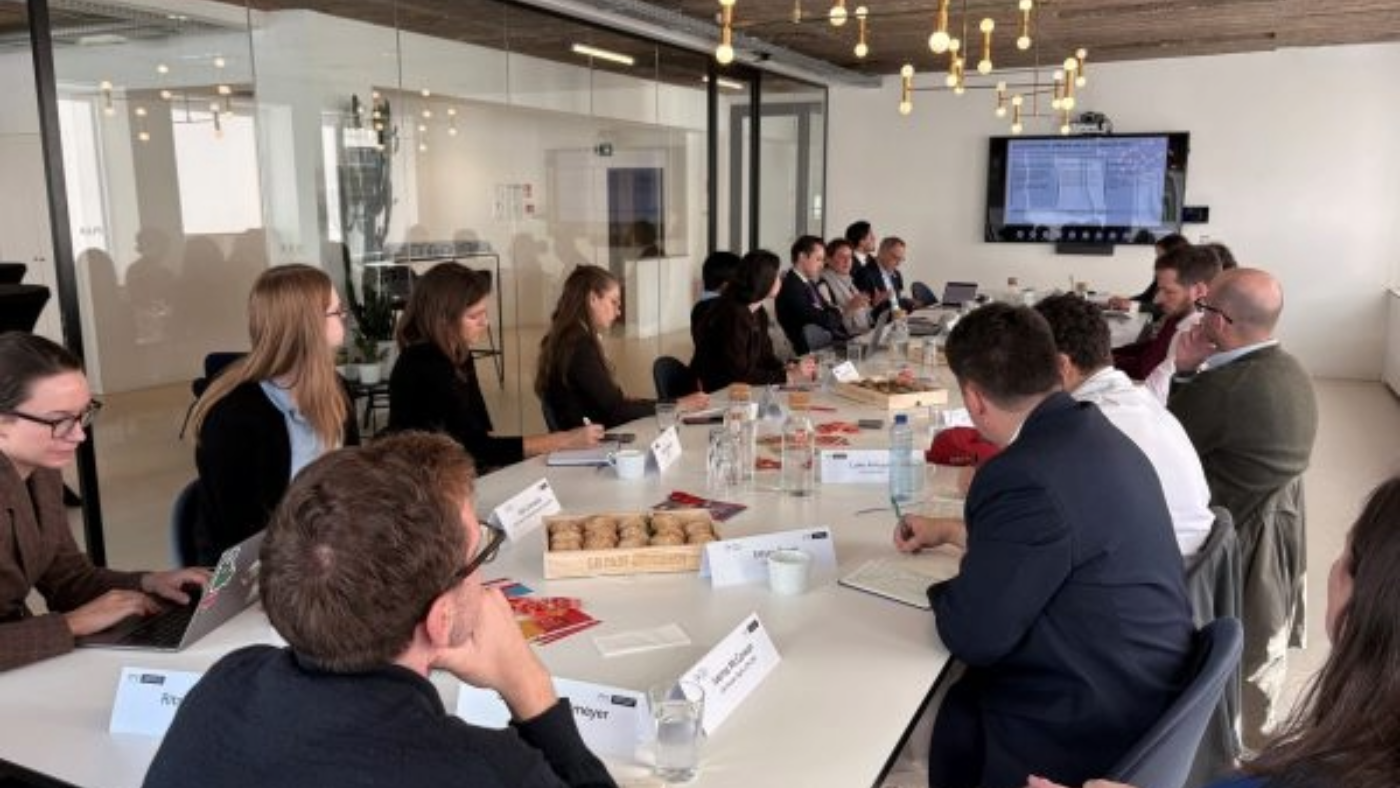
At the hybrid roundtable “Post-Quantum Ready – Securing Encryption for Connected Mobility,” held in Brussels ahead of Global Encryption Day 2026 and organized by eco’s Mobility Competence Group and Quantum Initiative on October 14, 2026, European policymakers, industry representatives, and cybersecurity experts discussed how connected mobility can prepare for post-quantum cryptography (PQC).
Contributions from the European Commission’s DG CONNECT, Data Warehouse GmbH, Google, and IBM highlighted the technical, industrial, and organizational challenges of this transition.
Long vehicle lifecycles meet the quantum challenge
Vehicles entering the market in the coming years may remain operational well into the 2040s, when advances in quantum computing could undermine widely used public-key cryptography.

For connected vehicles, the implications extend beyond data confidentiality. Secure software updates, digital identities, vehicle authentication, and vehicle-to-everything (V2X) communications all depend on cryptographic mechanisms that must remain trustworthy throughout a vehicle’s lifetime.
In safety-critical applications, however, the transition is not straightforward.
“Post-quantum signatures cannot simply be dropped into existing V2X systems. Their significantly larger size creates new challenges for bandwidth and communication performance, making hybrid approaches essential to the transition.”
— Stefan Bogensberger, European Commission, DG CONNECT
In V2X systems, where vehicles and infrastructure exchange time-sensitive information, cryptographic changes must preserve both security and performance. Hybrid approaches and crypto agility – the ability to update or replace cryptographic mechanisms as requirements evolve – are therefore important considerations for future vehicle architectures.
European technological sovereignty and supply-chain security
The transition also raises questions about Europe’s dependence on international technology providers.
As Bogensberger outlined, European vehicle manufacturers rely heavily on non-European suppliers for automotive software, semiconductors, cloud infrastructure, and autonomous-driving technologies. These dependencies affect not only competitiveness but also manufacturers’ ability to maintain secure systems throughout their operational lifetime.
European initiatives such as the European Connected and Autonomous Vehicle Alliance (ECAVA) seek to strengthen cooperation on software-defined vehicles, automotive hardware, artificial intelligence and autonomous-driving deployment.
A central consideration is integrating cybersecurity into technology development from the outset, rather than treating it as a final compliance check. Cryptographic capabilities built into hardware, for example, may be difficult to change once vehicles are deployed.
From European PQC roadmaps to practical migration
The EU’s approach emphasizes coordinated, risk-based migration. Its post-quantum transition roadmap prioritizes high-risk use cases for migration by 2030 rather than requiring every system to migrate simultaneously.
During the discussion, the importance of coordinating migration across the entire supply chain was emphasized:
“The entire supply chain needs to move together. Securing individual systems is not enough if critical dependencies remain vulnerable. A coordinated transition is essential.”
— Alessia Bizzarri, Head of Emerging Technologies Strategic Oversight Sector, European Commission, DG CONNECT
For automotive manufacturers, this means understanding not only their own cryptographic systems but also the security capabilities and migration plans of their suppliers.
A comprehensive cryptographic inventory is an essential starting point. However, maintaining an accurate overview can be difficult when security mechanisms are distributed across hardware, firmware, software, legacy systems, and third-party services:
“Cryptographic infrastructure is a moving target. Firmware updates, legacy systems and third-party dependencies constantly change the security landscape. Organizations need continuous visibility into their cryptographic assets to manage the transition effectively.”
— Matthias Reidans, Data Warehouse GmbH
Such inventories help organizations identify vulnerabilities, prioritize critical assets and develop migration plans.
Yet awareness of the risks does not automatically translate into action. For many companies, the challenge is knowing where to begin and how to translate migration requirements into practical steps:
“The question companies are asking is no longer just why they need to migrate, but where to start and how to do it. Raising awareness is important, but organizations also need practical guidance and tools to take their first steps.”
— Rita Jonusaite, Google
This points to the need for accessible tools, practical guidance and opportunities to share experience across sectors, particularly for smaller companies with limited specialist resources.
Preparing today for secure mobility tomorrow
Post-quantum readiness cannot be achieved by simply replacing encryption algorithms. It requires long-term planning and adaptable security architectures. The discussion also highlighted that migration extends beyond specialist cybersecurity teams.
“Post-quantum migration is not just a technical challenge for cryptographers. It is a complex coordination effort across the entire supply chain, involving technology providers, customers and business leadership.”
— Yana Humen, IBM
Organizations must understand their suppliers’ capabilities and timelines while involving IT, cybersecurity, legal teams and business leadership in migration planning.
Importantly, companies need not wait for every supplier to complete its transition. They can already identify cryptographic dependencies, assess high-risk use cases and begin developing migration strategies.
For Europe’s connected mobility ecosystem, the priority is to identify critical dependencies, assess long-term risks, and build adaptability into future vehicle architectures.
Through its Mobility Competence Group and Quantum Initiative, eco facilitates dialogue between industry, policymakers, and the technical community on secure and resilient digital infrastructures.
Get involved in eco’s Mobility Competence Group and Quantum Initiative
Interested in exchanging ideas with industry experts on connected mobility, cybersecurity, and quantum technologies? Learn more about eco’s Mobility Competence Group and the Quantum Initiative, or get in touch.
📚 Citation:
Trinkaus, Patricia. (October 2026). Post-Quantum Ready: Why Europe’s Connected Vehicles Need Future-Proof Encryption Today. dotmagazine. https://www.dotmagazine.online/issues/security-compliance-digital-sovereignty/post-quantum-cryptography-connected-vehicles
Patricia Trinkaus is Manager DBM & Technology at eco – Association of the Internet Industry, where she leads the IoT, Mobility and Email Competence Groups. She facilitates collaboration between industry experts, policymakers and technology stakeholders to address emerging technological developments and regulatory challenges. Her work focuses on fostering knowledge exchange, strengthening industry cooperation and advancing innovation across the digital ecosystem.
Connected vehicles rely on cryptographic systems to protect communication, software updates, and safety-critical functions. In her article for dotmagazine, published by eco – Association of the Internet Industry, Patricia Trinkaus of eco explains why preparing for future quantum computing threats is important for the long-term security of connected mobility.
Post-quantum cryptographic methods can require more data and processing resources, creating challenges for vehicle-to-everything (V2X) communication and existing vehicle systems. Patricia Trinkaus of eco highlights these technical constraints in dotmagazine, published by eco – Association of the Internet Industry, alongside the need for coordinated migration across automotive supply chains.
Companies can begin by identifying where cryptography is used, assessing vulnerable systems, and coordinating migration plans with technology suppliers. In dotmagazine, published by eco – Association of the Internet Industry, eco's Patricia Trinkaus emphasizes the importance of cryptographic inventories, practical guidance, and long-term planning.
Hybrid approaches combine existing cryptographic methods with post-quantum mechanisms, helping organizations introduce new protections while managing compatibility and performance constraints. Patricia Trinkaus of eco discusses this challenge in her dotmagazine article, published by eco – Association of the Internet Industry, particularly in relation to the bandwidth and communication requirements of V2X systems.